Domain hijacking is unauthorized control of a registration or its critical settings. Attackers may steal credentials, compromise email, abuse support recovery or manipulate staff. Because DNS controls web and mail routing, a takeover can affect the whole digital identity.
How takeover happens
Common paths include password reuse, phishing, compromised recovery email, social engineering and excessive administrator access. A registrar transfer is not required; changing nameservers alone can redirect users and mail.
- Treat registrar access as privileged infrastructure.
- Protect recovery email independently.
- Review API keys and agency access.
Layer the preventive controls
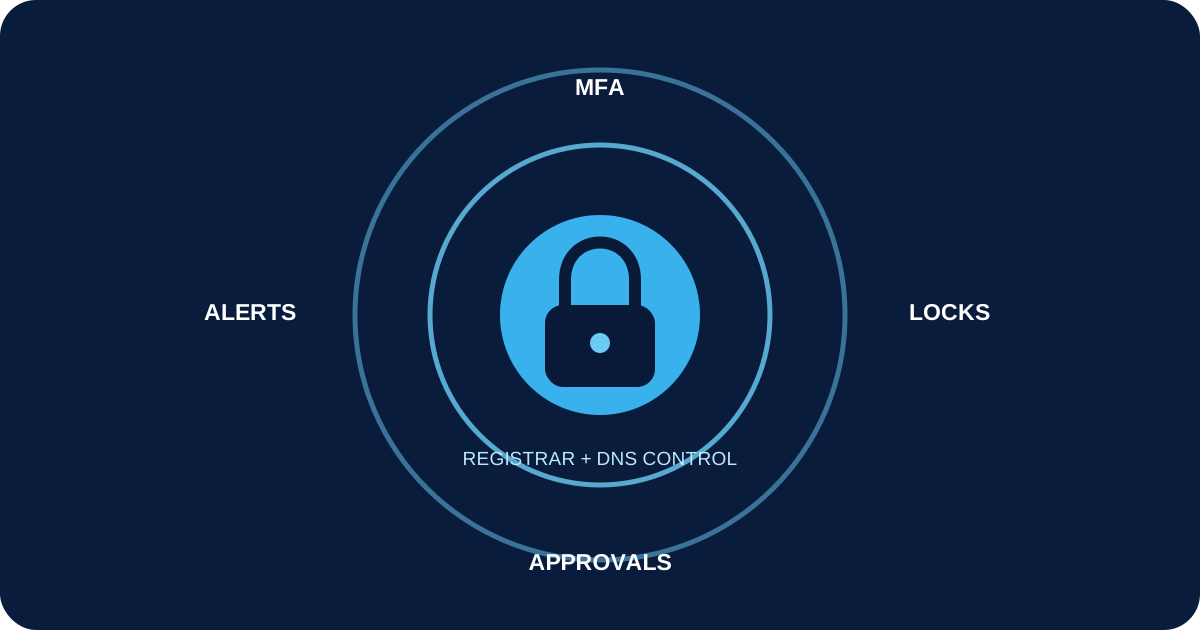
Use unique credentials, phishing-resistant MFA where available, registrar and transfer locks, role-based accounts and change alerts. Keep registrant data accurate so legitimate recovery remains possible.
- Require two-person approval for critical changes.
- Restrict DNS API tokens to needed zones and actions.
- Test backup contacts and recovery codes.
Respond to suspected hijacking
Contact the registrar through a known channel immediately, preserve evidence and notify security, legal and communication owners. Verify DNS, registration status, email routing, certificates and third-party logins that depend on the domain.
- Freeze related account changes.
- Recover registrar and email access.
- Restore known-good DNS and validate services.
- Reset dependent credentials and document the timeline.
Frequently asked questions
Is transfer lock enough?
No. It can help prevent transfer, but compromised users may still change DNS or contacts. Use layered account and approval controls.
Can Cloudflare WAF stop domain hijacking?
A WAF protects proxied web traffic, not registrar-account ownership. Secure the registrar, recovery email and DNS control plane separately.
What is the first sign of a takeover?
Unexpected login, contact, nameserver, DNS or certificate changes are strong indicators. Alerts should reach more than one trusted person.